99.3% exam pass rateAll candidates since 2023, PECB exams.
Get your team fluent in the frameworks that run the business.
Cyber, GRC and AI governance certifications, taught by a working CISO. Live cohorts on confirmed dates, self-paced any time, in-house when it makes sense.
0+
Professionals trained
Across Europe, in person and online
0
Accredited training ecosystems
PECB and ISACA official programmes
0+
Cohorts completed
Live cohorts and in-house
Live · Confirmed dates
Upcoming confirmed sessions.
November 2026
5 days
€2,999
December 2026
4 days
€2,900
4 days
€2,900
Why Cyber Academy
Trainers who run what they teach.
Cyber Academy is led by active GRC practitioners, including a working CISO. Trainer experience and course ownership are shown for the relevant programme. Three commitments guide our delivery:
- Practitioner-led delivery, with trainer experience shown for each confirmed programme.
- Published standard-course prices shown up front; tailored scopes are quoted.
- We map you to the path that fits, not the one that sells
Why Cyber Academy
Practitioner-led delivery, with trainer experience shown for each confirmed programme.
Current GRC priorities
What teams
are training on right now.
Six topics where regulators, auditors and boards are putting pressure today. Pick the one your audit is landing on; there's a certification path waiting.
Scope varies by jurisdiction
NIS 2
Risk treatment, incident reporting and supply-chain duties under NIS 2, with scope and national implementation varying by jurisdiction.
See coursesFinancial entities
DORA
Operational resilience for financial entities: third-party registers, ICT risk and threat-led testing, mapped where useful to ISO 27001.
See coursesPhased obligations
AI Act
Risk classification, ISO 42001 management system, transparency duties for general-purpose AI.
See coursesThe classic
ISO 27001
The reference standard for ISMS. Compare Foundation, Lead Implementer, Lead Auditor and ISO 27005 risk-management paths.
See coursesCross-cutting
GDPR & privacy
Records of processing, DPIA, lawful basis, AI Act interaction, CDPSE preparation. What changed since 2018, what auditors check now.
See coursesRisk method
ISO 31000
Enterprise risk management. Foundation, Risk Manager, Lead Risk Manager. Complements ISO 27005 and EBIOS RM.
See courses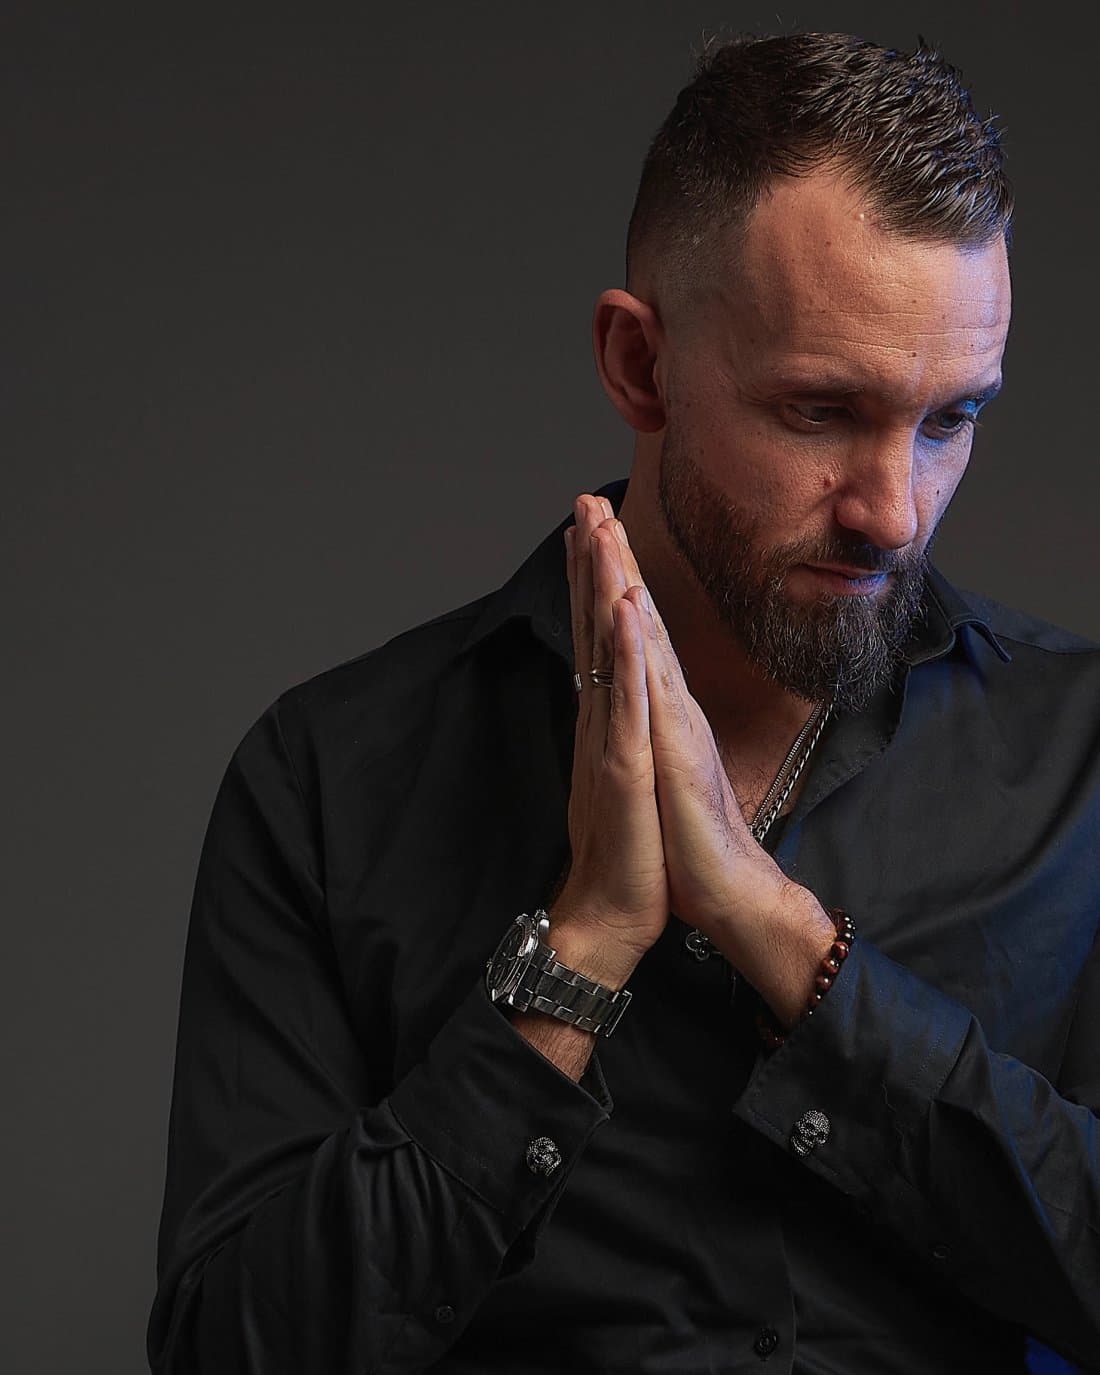
Lead trainer
Christophe Mazzola
Active CISO · 20+ certifications
10+
years in the field
Your trainers
A small team. One bar.
Cyber Academy was founded by Christophe Mazzola, an active CISO and author of Être en Cybersécurité. He continues to lead delivery with a small team, matching trainers to subjects they actively practise and naming the trainer when confirmed.
- Active practitioners
- Audit-ready exercises
- Real findings, not slides
They trust us
The organisations that train with us.
From these companies and many more, in person and online, across Europe.
Testimonials
What clients say after they pass.
Field notes
Latest from the GRC trenches.

05 Oct 2026
The Risk That We Don't Have MFA
Two weeks of ISO 27001 audits and the same mistake in almost every risk register; here's why it keeps happening, and why your spreadsheet is part of it.
 Written by Christophe Mazzola

28 Sept 2026
ISO 9001:2026 Is Out. Here Is What Actually Changed.
The sixth edition of ISO 9001 was published on 16 September 2026. Quality culture becomes a requirement, risks and opportunities finally split, and the documented information wording shifts. A practitioner's read, clause by clause, with the transition dates.
Written by Christophe Mazzola
21 Sept 2026
“We Have an AI Policy.” Where’s the Inventory?
An approved-tools list does not tell you how AI is used. Here is how to build an inventory that captures shadow AI, misuse of approved tools and real data flows, and an AI bill of materials that tells you what sits underneath.
Written by Christophe MazzolaThe GRC Brief
Five links, one short take. Monday at 8am.
What landed in regulation last week, the audit finding worth remembering, the template you can lift today. Written by our practitioners. Three-minute read.
Before you bookSix honest answers,
Six honest answers,
before you commit.
Recognition, picking the right path, what happens if you fail, how to invoice, audit pressure, prices. The same questions every learner sends us. Read them, then book the cohort that fits.
Yes. We deliver official PECB and ISACA training tracks used internationally. The credential is issued by the relevant certification body, not by Cyber Academy.
Each course page lists prerequisites, target audience, and a 'when NOT to take it' section. If you're still unsure, book a free 20-minute discovery call: we'll match you to the path that fits your role, deadline and budget. We'd rather lose the sale than place you in the wrong cohort.
PECB and ISACA re-sit conditions vary by programme. We explain the applicable exam policy before purchase and provide targeted preparation when a re-sit is needed.
Yes. We invoice companies directly with VAT-compliant documents (or VAT-free under our Gran Canaria registration, depending on your tax rules). Billing terms, group pricing and the availability of a dedicated in-house cohort depend on the course and scope; they are confirmed on the course page, in the written proposal or the order summary. Send your requirement to [email protected] and we will scope it.
We run live cohorts every month and can confirm a private session for your team within 2 to 3 weeks if dates are tight. For a hard deadline (DORA Article 28, NIS 2 transposition, etc.), tell us in the first email and we'll prioritise scheduling and content tailored to your audit scope.
Yes. Current standard live and self-paced prices are published in EUR where a course can be booked directly. In-house, multi-seat and custom scopes receive an itemised quote because format, dates and headcount vary.
Pick a path.
Book a date.
Confirmed cohorts on real calendars. Prices on the page. Exam and re-sit terms shown before purchase.